
- Home
- Tutorials
- Cybersecurity
- DevSecOps CI/CD
DevSecOps: Shift-Left Security Automation in CI/CD Pipelines
Historically, software security was treated as a separate, manual bottleneck at the very end of the development lifecycle: after months of coding, an external penetration testing firm spent two weeks auditing the staging server right before production launch, creating massive deployment delays and friction. DevSecOps (Development, Security, and Operations) integrates security testing automatically into every phase of the software delivery lifecycle—from initial developer code commits to automated CI/CD builds.
The "Shift-Left" Philosophy
The core philosophy of DevSecOps is Shift-Left: moving security checks as early (leftwards) on the software timeline as possible. Discovering and remediating a SQL injection flaw in an IDE pre-commit hook takes 5 minutes and costs virtually zero dollars; fixing that same vulnerability after a public ransomware breach costs millions in forensic investigation, legal liability, and brand degradation.
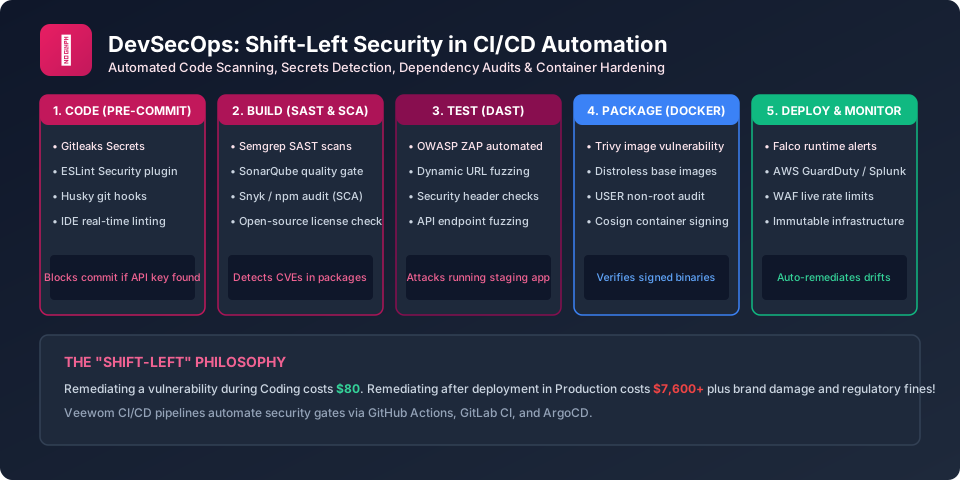
Figure 37.1: The 5-Phase DevSecOps Automated CI/CD Pipeline Architecture
Automated Security Testing Stages in CI/CD
| Testing Category | Acronym | When It Runs | What It Evaluates | Leading Tools |
|---|---|---|---|---|
| Secret Detection | - | Pre-commit Git Hook & Pull Request | Scans commits for accidentally hardcoded AWS API keys, private keys, and database passwords. | Gitleaks, TruffleHog |
| Static Analysis | SAST | Build Phase (on compile) | Parses raw uncompiled source code to find architectural flaws (SQLi, XSS, unescaped queries). | Semgrep, SonarQube, CodeQL |
| Software Composition | SCA | Build Phase (Package Resolution) | Scans third-party open-source dependencies (npm, pip, maven) against known CVE databases. | Snyk, OWASP Dependency-Check |
| Dynamic Analysis | DAST | Test / Staging Phase | Attacks the running web application from the outside, injecting active payloads to verify exploitable bugs. | OWASP ZAP, Burp Suite Enterprise |
| Container Scanning | - | Packaging Phase (Docker image) | Scans container base OS packages and configuration misconfigurations. | Trivy, Grype |
Implementing an Automated Security Gate in GitHub Actions
Here is a production GitHub Actions workflow that executes automated secret scanning and SAST checks on every pull request:
.github/workflows/security.yml
name: "DevSecOps Automated Security Gate"
on: [push, pull_request]

jobs:
  security-audit:
    runs-on: ubuntu-latest
    steps:
      - name: Checkout Source Code
        uses: actions/checkout@v4
        with:
          fetch-depth: 0

      # 1. Block hardcoded secrets
      - name: Run Gitleaks Secret Scanner
        uses: gitleaks/gitleaks-action@v2
        env:
          GITHUB_TOKEN: ${{ secrets.GITHUB_TOKEN }}

      # 2. Run Semgrep SAST Analysis
      - name: Run Semgrep SAST
        run: |
          python3 -m pip install semgrep
          semgrep scan --config=auto --error

      # 3. Audit NPM Dependencies for Known CVEs
      - name: Run NPM Audit
        run: npm audit --audit-level=high
Frequently Asked Questions (FAQ) - Student & Interview Review
Q1. What does 'Breaking the Build' mean in DevSecOps?
Q2. What is the difference between SAST and DAST?
Explore Related Cybersecurity Tutorials & Next Steps
Broaden your defensive and offensive security knowledge across our curriculum:
Integrating Semgrep, OWASP ZAP, and Snyk into automated CI/CD security gates.
Scanning container images with Trivy and signing images with Cosign in CI/CD.
Running npm audit and pre-commit Husky git hooks to block secret commits.
Interview questions explaining Shift-Left security, breaking builds, and SAST vs DAST.


You may also like this!
© Veewom.com. | Managed by PinePL
